Ferry
A rule-based proxy client for macOS. Send every connection where it belongs: direct, through a proxy, out a LAN gateway, or via another device in your mesh.
A rule-based proxy client for macOS. Send every connection where it belongs: direct, through a proxy, out a LAN gateway, or via another device in your mesh.
One client that scales from a single Mac to taking over the whole LAN.
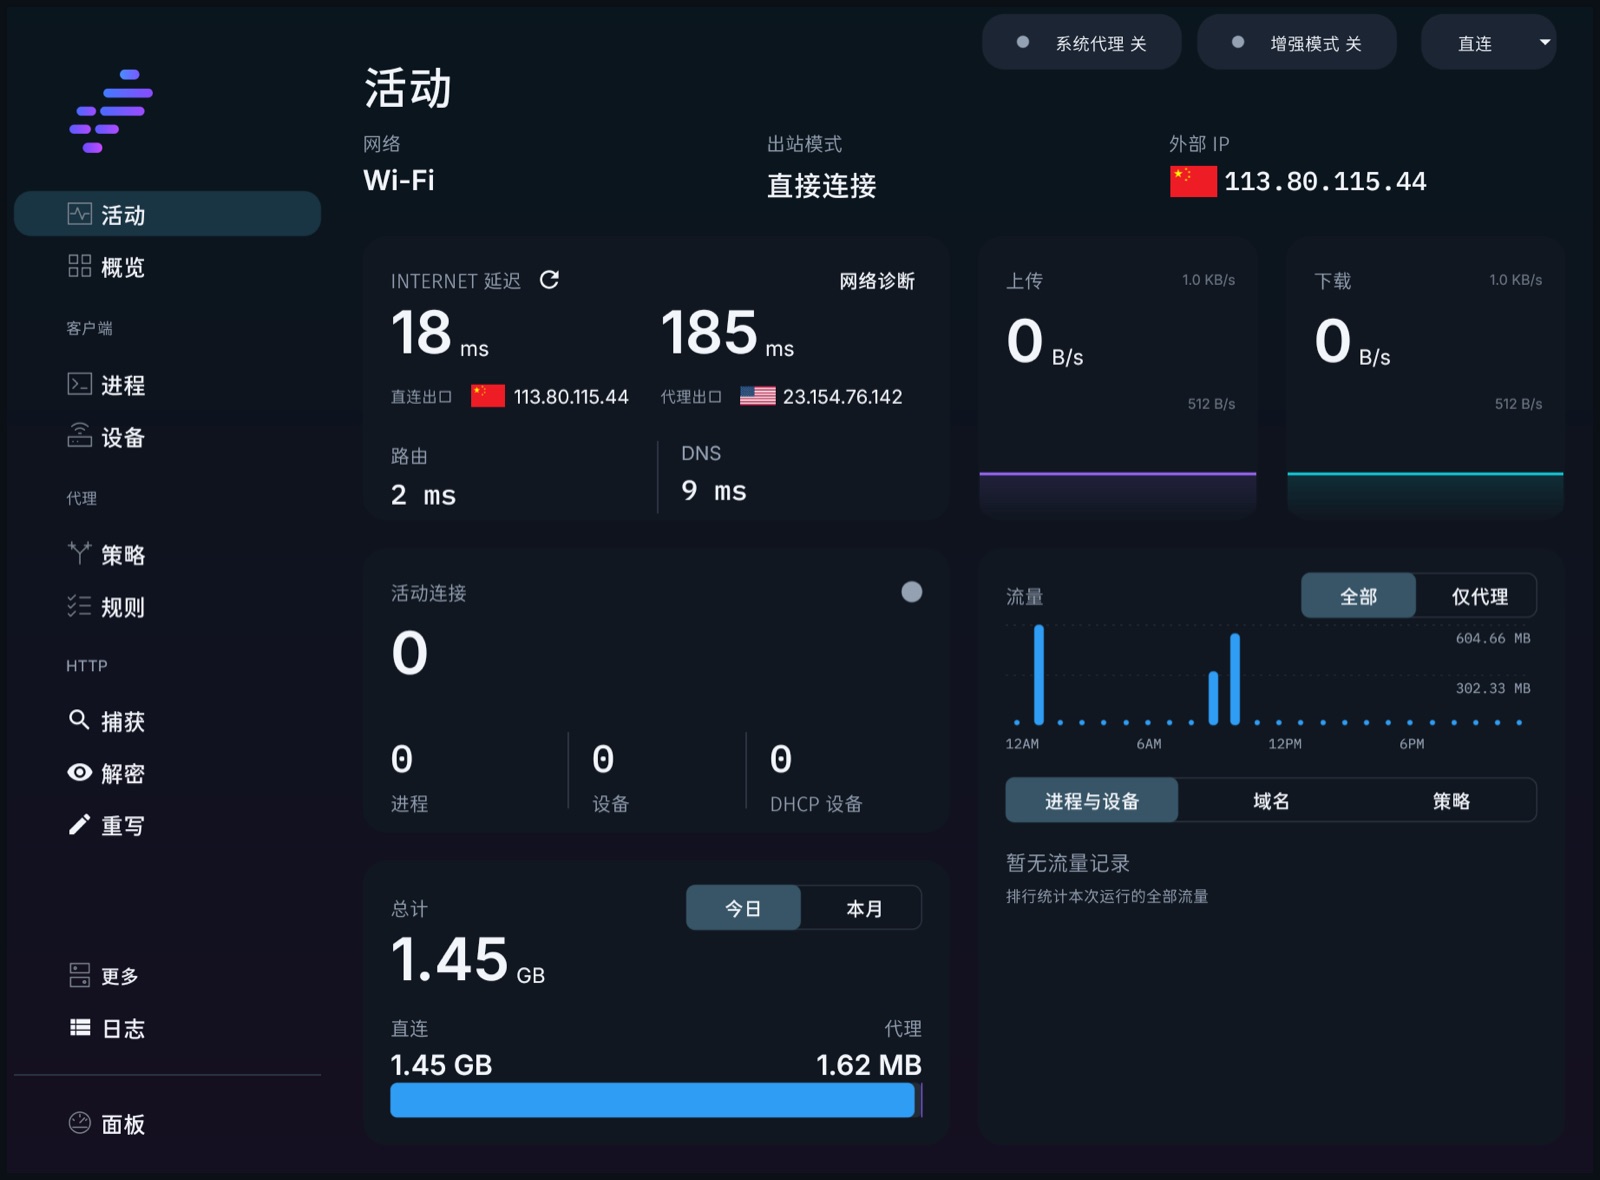
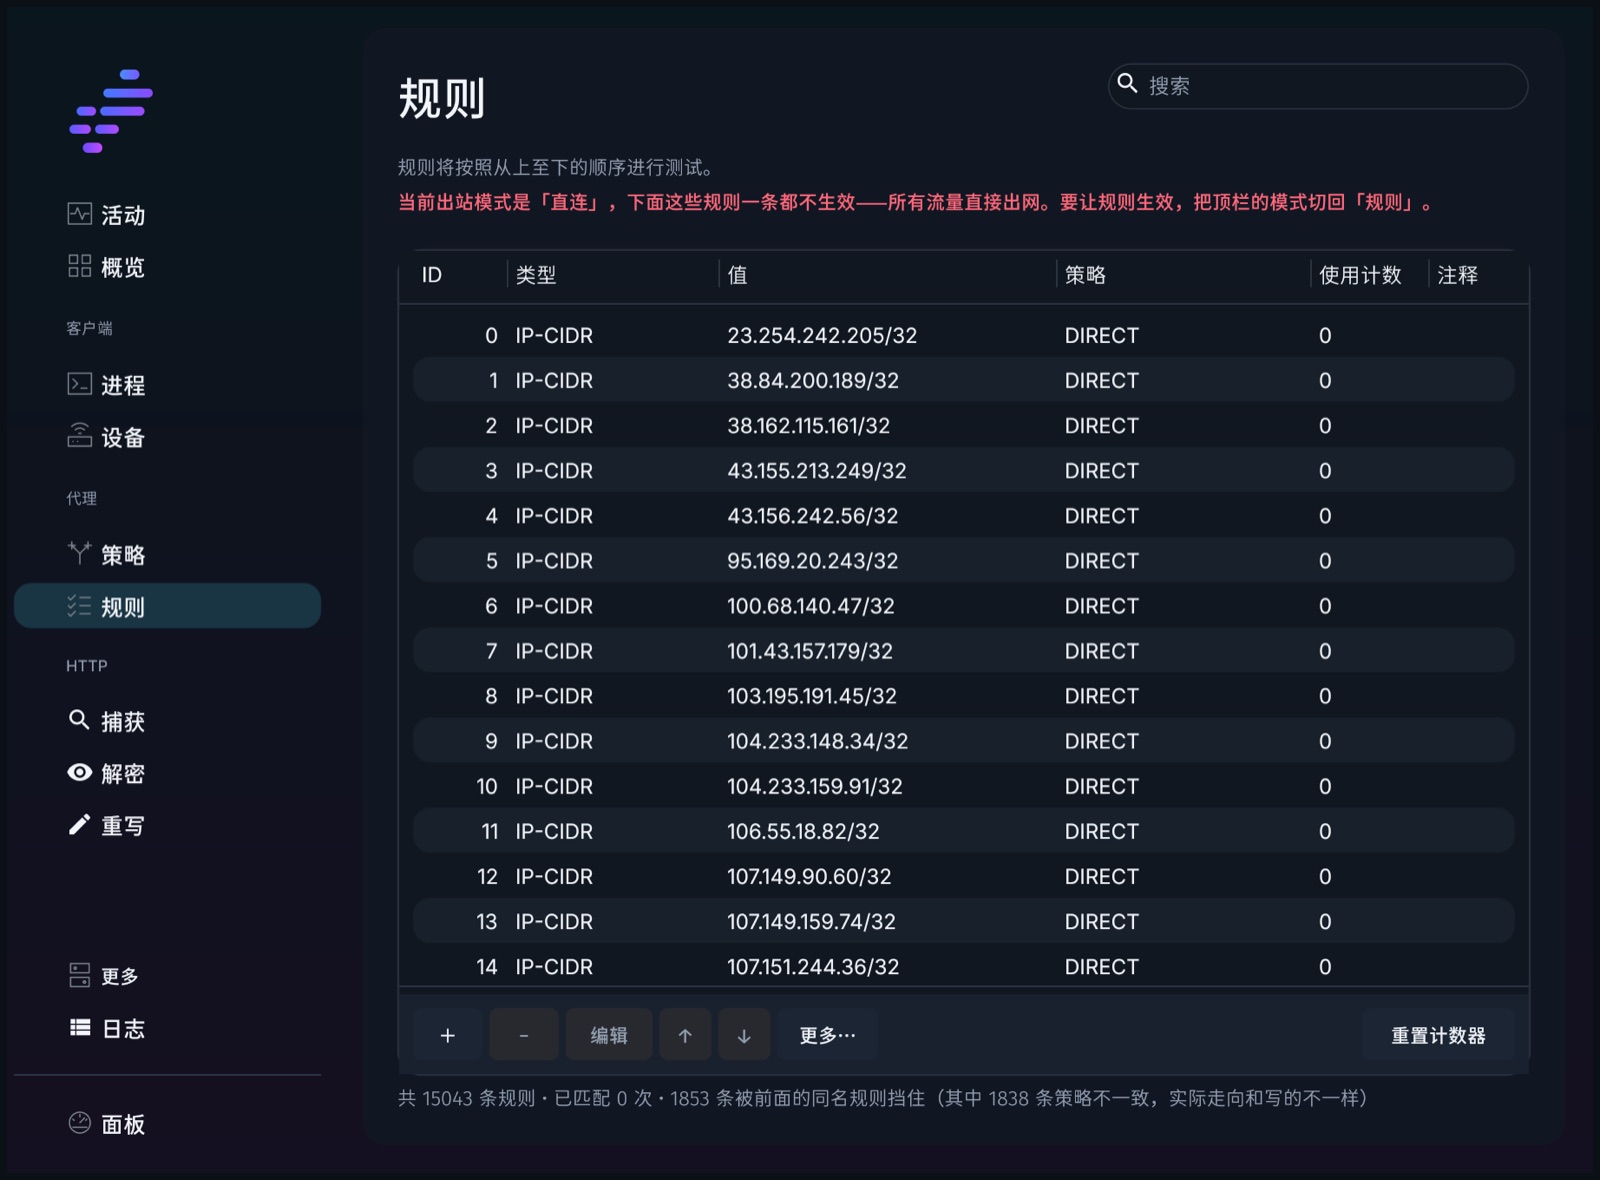
Clash-compatible rules and subscriptions. Route by domain, IP, GEOIP or process. Shadowed and duplicate rules are flagged at a glance.
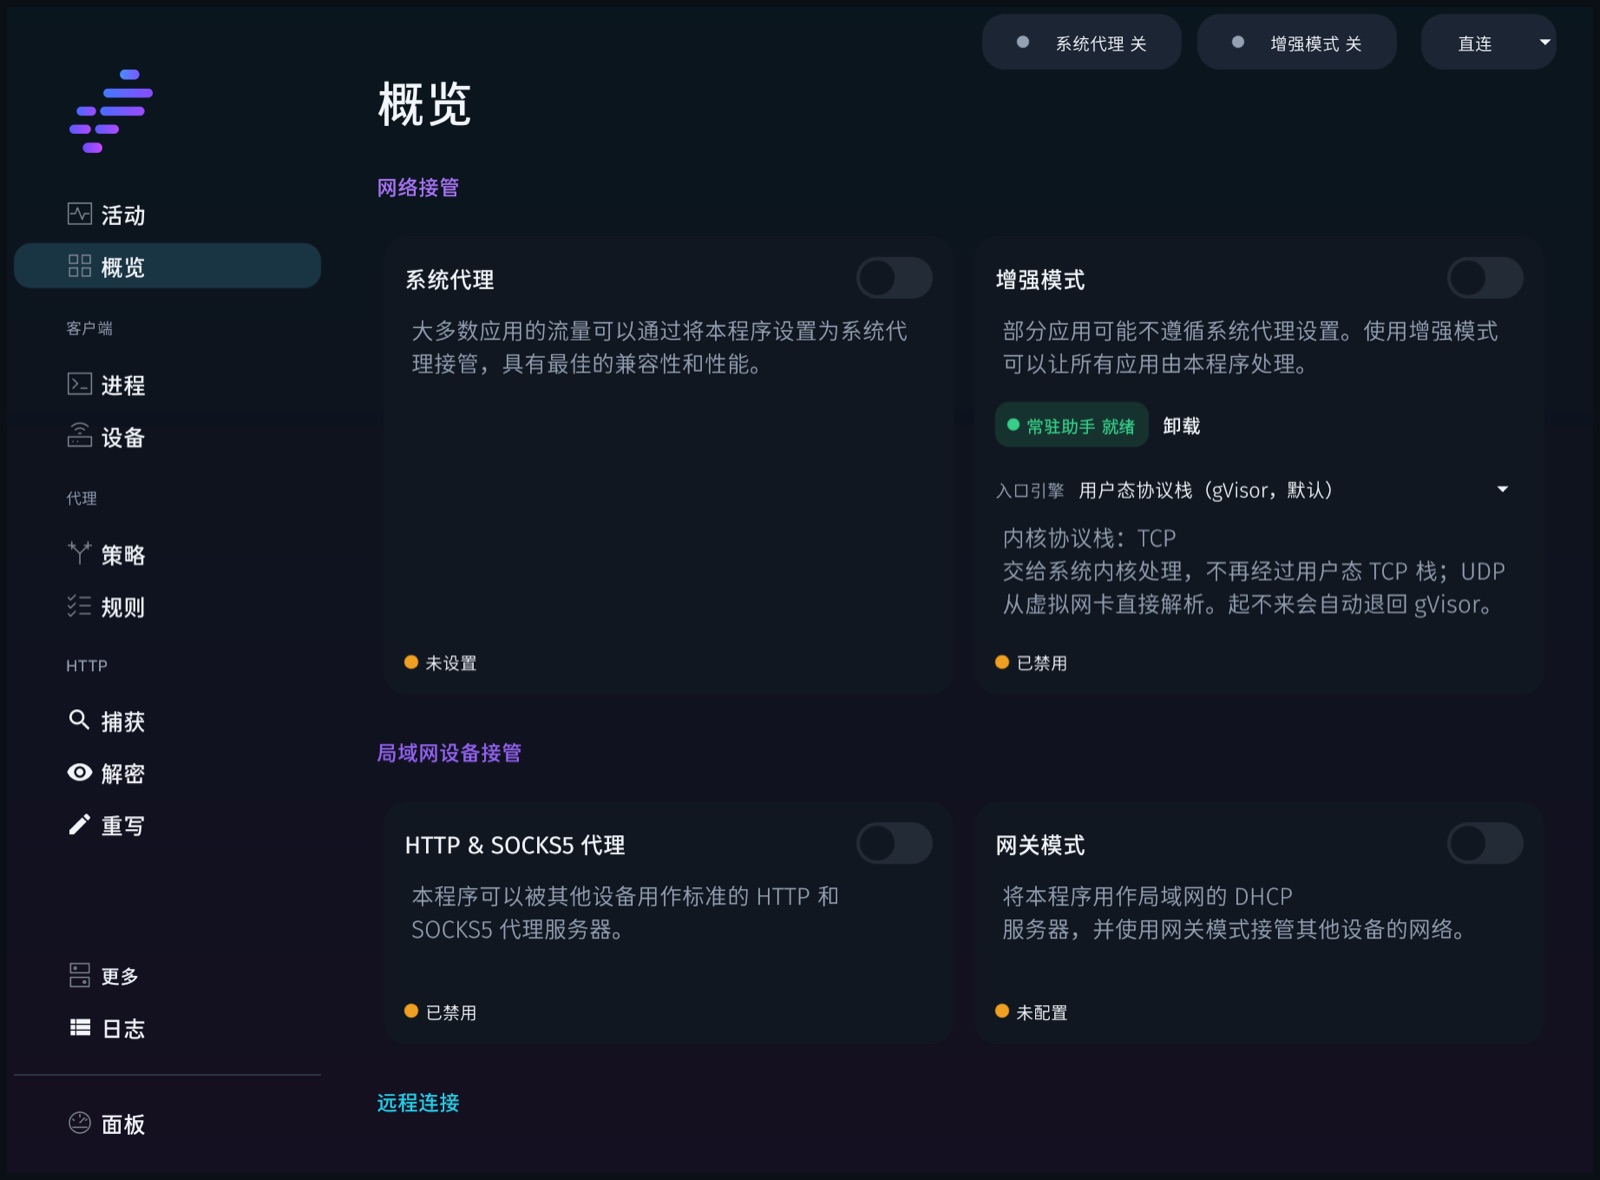
A virtual NIC captures all traffic, including apps that ignore the system proxy. Choose a userspace or kernel network stack as the inbound engine.
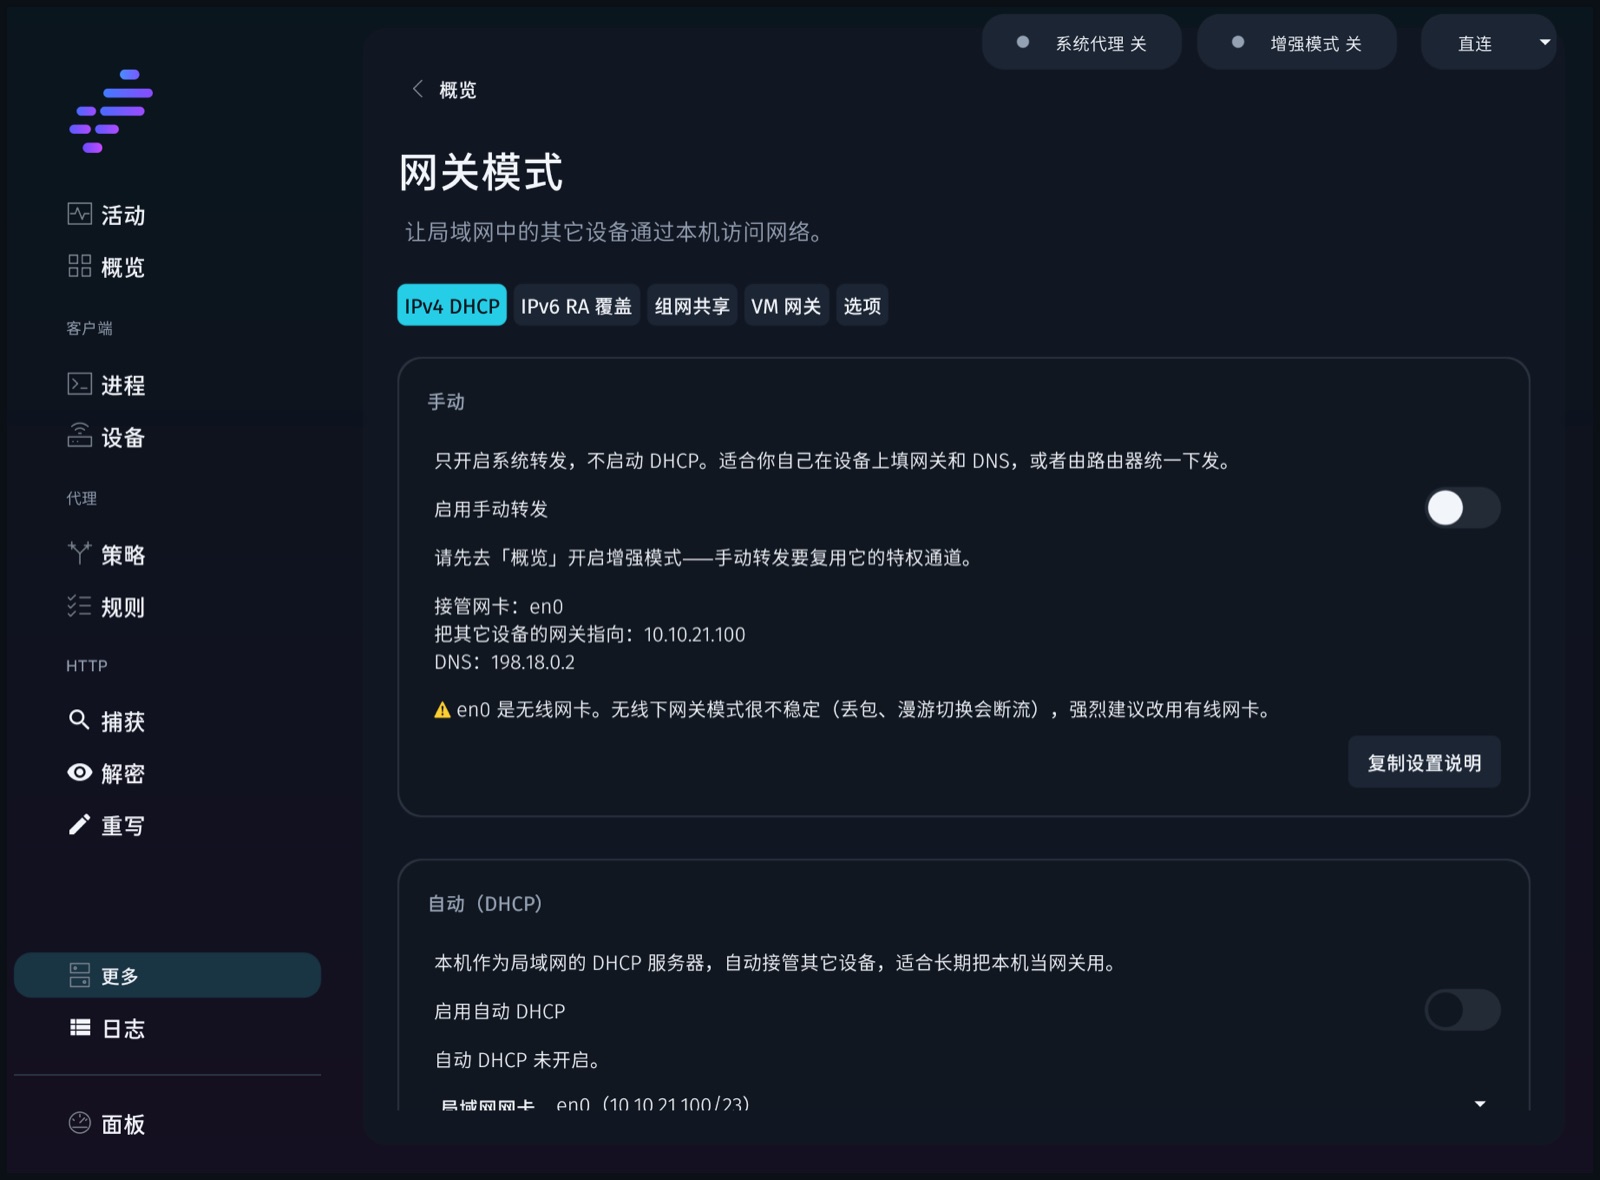
Act as the LAN’s DHCP server and gateway to take over other devices; hijack hard-coded DNS, override IPv6 RA, toggle devices one by one.
A built-in Tailscale client joins a headscale network and lets any device on it serve as a proxy exit; as a gateway, share your LAN with the mesh.
Share links, subscription URLs, Clash YAML, Surge configs and WireGuard .conf files: paste or drop them in and Ferry recognises them, explaining anything it can’t.
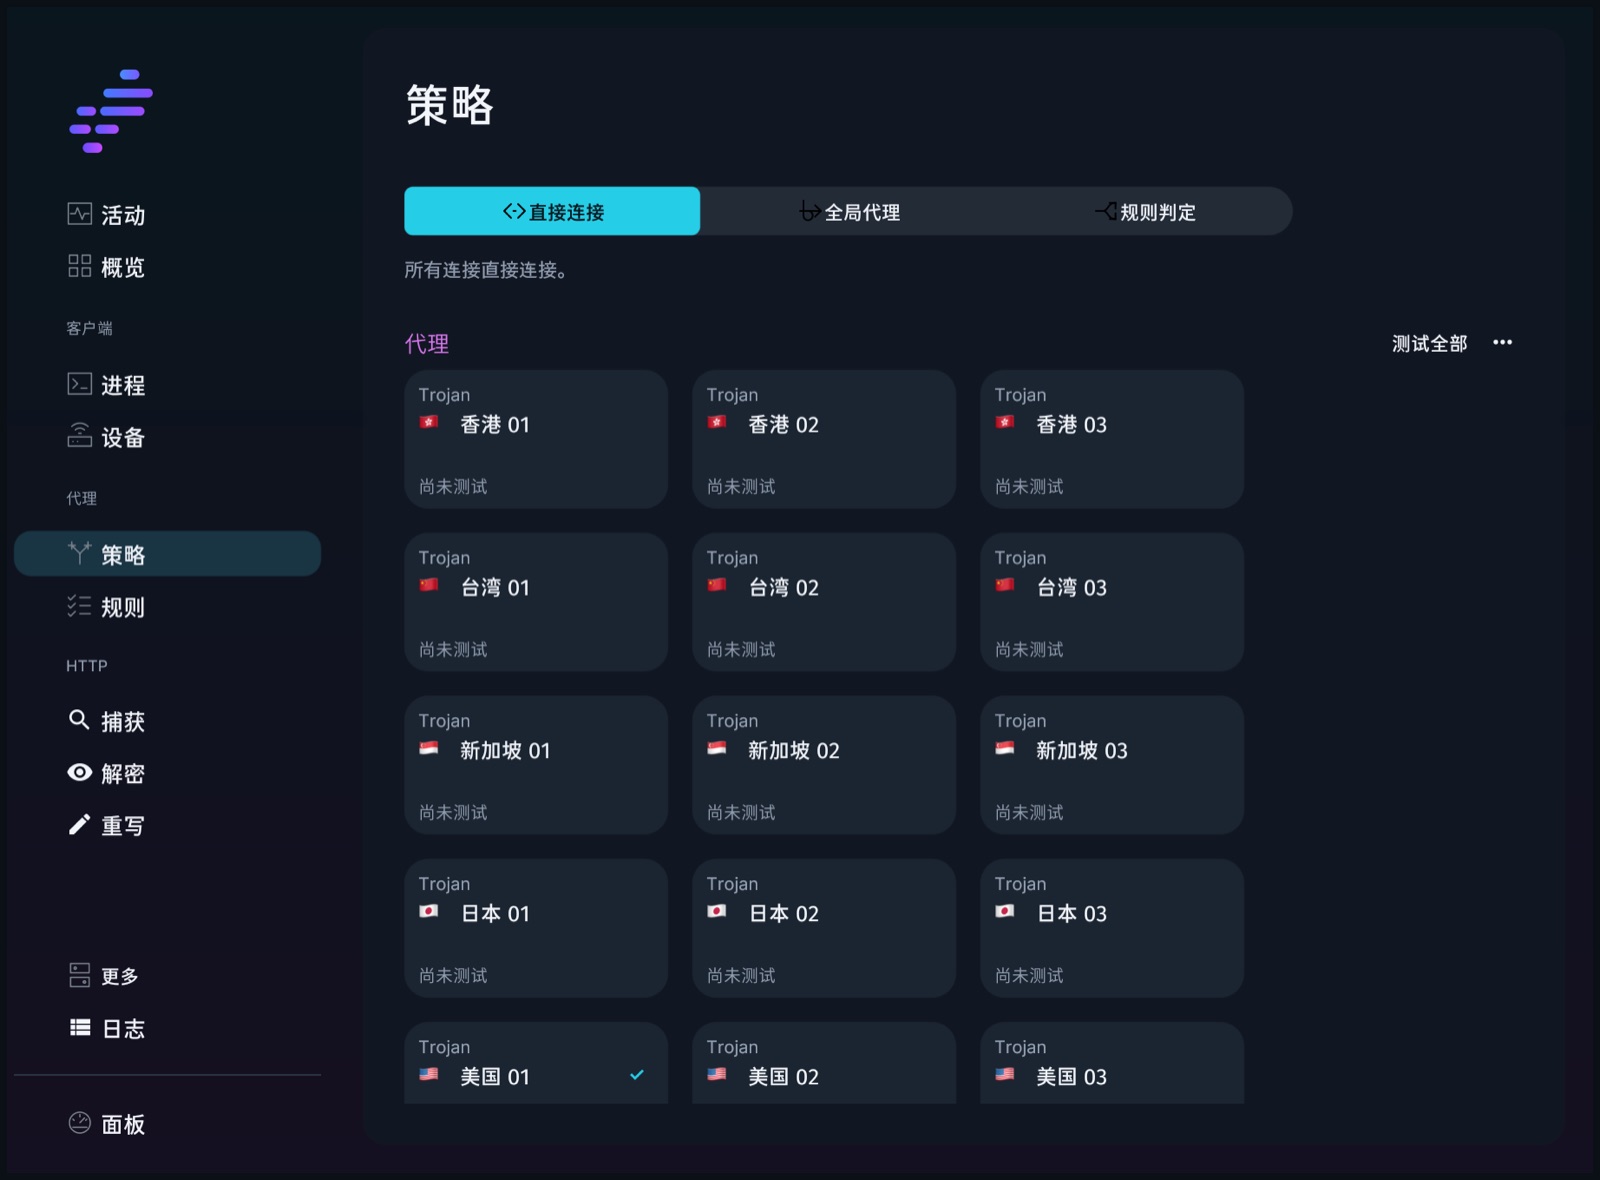
Shadowsocks, VMess, VLESS (incl. Reality), Trojan, Hysteria 2, WireGuard, SOCKS5, HTTP. Dialer proxies and per-node latency test URLs.
Same yardstick as Clash: two requests on one connection, only the second one counts, so handshakes never inflate the number.
HTTP capture with filters, MitM decryption of HTTPS, request and response rewriting, with local processes identified by app.
Switch scenes automatically by Wi-Fi or interface; an HTTP API and web panel let you check status and switch policies from your phone.
Dark, restrained, information-dense. Every dialog shares one style.
macOS 13 or later, Apple Silicon. Once installed, Ferry checks for updates and upgrades itself in one click.
Fetching the latest version…
What changed in each release, written at publish time.